ESSENTIAL GUIDANCE · PENETRATION TESTING · 10 min read
Part of Validate insights →Understanding Penetration Testing: A Comprehensive Guide
Penetration testing is a controlled way to find weaknesses before attackers do. It uses authorised, real-world security techniques to assess systems, networks, websites and applications, then turns the findings into practical remediation work. For organisations that rely on digital services, cyber security penetration testing is not just a technical exercise; it is a way to protect operations, customer trust and sensitive data.
Technical review lead: James Hinton · Offensive security lead
What is penetration testing in software testing?
Penetration testing in software testing is a security assessment that actively checks whether weaknesses in an application, website, network or system can be exploited. Unlike functional testing, which asks “does this feature work?”, penetration testing asks “could someone abuse this feature, configuration or connection?” A skilled penetration tester thinks like an attacker, but works within an agreed scope, with permission and clear rules of engagement.
The goal is not to “break things” for the sake of it. The goal is to understand risk in context. A vulnerability that looks minor in a scan may become serious if it gives access to sensitive data, allows privilege escalation or helps an attacker move deeper into the environment. That is why good penetration testing combines technical testing, judgement and clear reporting.
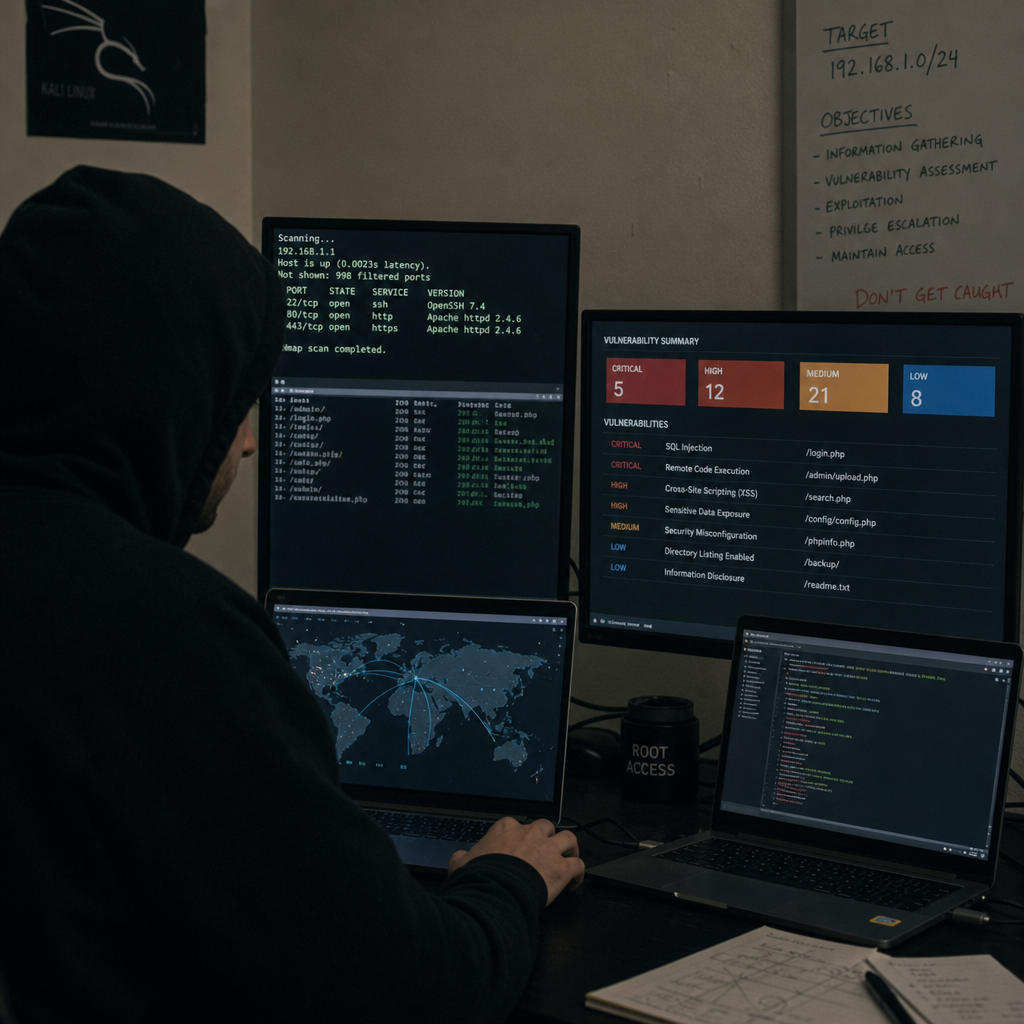
Penetration testing sits within a wider security strategy
A single test cannot guarantee complete security, but it can reveal the gaps that matter most. Penetration testing services are often used after major infrastructure changes, before a compliance review, before launching a new digital service, or as part of an ongoing security assurance programme.
It also helps bridge the gap between policy and reality. A firewall rule may look sensible on paper, but an external penetration testing exercise can show whether exposed services are visible from the internet. A password policy may seem adequate, but an internal network test may reveal shared credentials, weak hashes or poor segmentation.
Typical areas covered include:
- Networks: firewalls, routers, switches, servers, VPNs, cloud networking and exposed ports.
- Websites and applications: login flows, forms, APIs, session handling and access controls.
- People and processes: where approved, testing may include social engineering scenarios or checks on incident response.
- Physical and wireless environments: some engagements include office access controls, Wi-Fi security or device exposure.
This is where network penetration testing differs from website penetration testing or web penetration testing. Network testing focuses on the infrastructure that connects and protects systems, while web testing focuses on the logic, data handling and attack surface of web applications.
Network penetration testing focuses on the routes attackers use
Network penetration testing examines how an attacker might reach, enter and move through an organisation’s technical environment. It looks for open ports, unnecessary services, outdated software, misconfigured access controls, weak encryption, insecure protocols and credential weaknesses. It can also test how well segmentation prevents one compromised system from becoming a route to everything else.
There are two common perspectives: external and internal. External penetration testing simulates an attacker operating from outside the organisation, usually across internet-facing systems such as VPN gateways, mail servers, remote access portals, cloud services and public IP ranges. Internal testing starts from inside the network and explores what could happen if a malicious insider, compromised laptop or breached account gained a foothold.
Both matter because real incidents rarely follow one neat path. An attacker may begin externally, steal credentials, connect remotely and then move laterally. A good test helps show which controls slow that journey, which ones fail, and where the organisation should prioritise improvements.
How does a penetration test actually work?
A penetration test usually follows a structured lifecycle: scoping, reconnaissance, scanning, validation, exploitation, post-exploitation analysis and reporting. Each stage builds on the last, so the final result is more than a list of flaws; it is a practical picture of how risk could unfold in the real world.
Get a free copy of our penetration test scoping workbook
Completing this workbook does not authorise testing. Active testing requires explicit written permission from the relevant system owner.
Need help scoping your penetration test? Contact us for help →
1. Planning and scoping
The engagement begins with clear boundaries. The organisation and testing team agree what is in scope, what is out of scope, when testing can happen, who should be contacted if something unexpected occurs, and what level of exploitation is acceptable.
This stage is essential because penetration testing must be safe, authorised and proportionate. A production system, for example, may need careful handling to avoid disruption. The scope should also reflect the business objective, whether that is testing a new customer portal, checking external exposure or assessing internal resilience.
2. Reconnaissance and discovery
The tester gathers information about the target environment. For external work, this may include public records, domain information, exposed services and visible technologies. For internal work, it may include network ranges, host discovery, service enumeration and identity infrastructure review.
Reconnaissance helps the tester understand what an attacker would see first. It also prevents wasted effort. Instead of testing blindly, the penetration tester builds a map of likely entry points and areas worth deeper inspection.
3. Scanning and analysis
At this stage, automated tools help identify open ports, service versions, known vulnerabilities, certificates, protocols and configuration issues. However, this is where experience matters. Automated findings need validation because false positives can waste time, while false negatives can hide meaningful risk.
A vulnerability scanner may flag an outdated service. A tester asks what that service does, whether it is reachable, whether exploit code exists, whether compensating controls are present, and what impact compromise would have.
4. Exploitation and proof of impact
Where it is safe and permitted, the tester attempts to exploit selected weaknesses. This may involve bypassing authentication, cracking weak passwords, exploiting a vulnerable service, abusing misconfigured permissions or chaining several lower-risk issues into a more serious outcome.
The point is to prove impact without causing unnecessary damage. For example, a tester may demonstrate that access to a low-privilege account can lead to sensitive file shares, rather than copying large volumes of data. Evidence should be strong enough to support remediation, but controlled enough to protect the environment.
5. Reporting and remediation guidance
The final report should be clear to both technical and non-technical readers. It normally explains what was tested, what was found, how severe each issue is, what evidence supports the finding, and how to fix it.
The best reports do not stop at “patch this”. They explain root causes, business impact and practical next steps. A useful finding might recommend disabling an unnecessary service, enforcing multi-factor authentication, improving network segmentation, replacing weak cipher suites or tightening access control lists.
Penetration testing tools support expert judgement
Penetration testing tools help testers work efficiently, but they do not replace expertise. Tools produce signals; humans interpret them. The value comes from choosing the right tool, validating the output and understanding how one weakness may connect to another.
Common tools include:
- Nmap: used for host discovery, port scanning and service enumeration.
- Wireshark: useful for analysing network traffic and understanding protocols or suspicious behaviour.
- Metasploit: often used to validate exploitability in a controlled way.
- Burp Suite or OWASP ZAP: widely used in website penetration testing and web penetration testing for intercepting and testing web traffic.
- John the Ripper or Hashcat: used in approved scenarios to assess password strength and cracking resistance.
- Nessus, OpenVAS or similar scanners: used to identify known vulnerabilities that require human review.
A mature test does not rely on a single platform. For example, a network scan may identify an exposed service, packet analysis may show weak protocol use, and manual testing may confirm that access controls are poorly configured. The result is a more reliable view of risk than any one tool can provide.
Penetration testing is not the same as vulnerability scanning
Vulnerability scanning is broader, faster and more automated; penetration testing is deeper, more contextual and more adversarial. Scans are useful for routine hygiene because they can quickly flag missing patches, known CVEs, weak configurations and exposed services. Penetration testing goes further by asking whether those issues can be exploited and what the real consequence would be.
A useful comparison looks like this:
|
Area |
Vulnerability scanning |
Penetration testing |
|---|---|---|
|
Main purpose |
Identify potential weaknesses |
Validate exploitability and impact |
|
Method |
Mostly automated |
Manual and tool-assisted |
|
Depth |
Broad coverage |
Targeted investigation |
|
Output |
List of findings |
Risk narrative with evidence and remediation |
|
Best use |
Regular monitoring |
Assurance, compliance support and major change validation |
Both activities have a place. Scanning helps organisations keep watch continuously, while penetration testing gives a more realistic attacker’s-eye view. Treating them as interchangeable can create blind spots.
Choosing the right penetration testing services
The right provider should help you define a sensible scope, minimise disruption and produce findings your team can act on. Before booking a test, be clear about what you need to learn. Are you worried about internet-facing systems, internal lateral movement, a new web application, cloud infrastructure or regulatory expectations?
Use this checklist when evaluating penetration testing services:
- Scope clarity: Can they explain what will and will not be tested?
- Relevant experience: Do they understand your environment, technologies and risk profile?
- Methodology: Do they combine automated discovery with manual validation?
- Safety controls: Do they have escalation contacts, testing windows and rollback considerations?
- Reporting quality: Will the report include evidence, business impact and prioritised remediation?
- Retesting: Can they verify that fixes have worked after remediation?
- Communication: Will they brief stakeholders before, during and after the engagement?
Do not wait until an audit deadline or suspected breach forces your hand. If your organisation has recently changed infrastructure, launched a new website or exposed new services to the internet, book a penetration testing assessment now and get a clear view of your risk before an attacker does.
Common findings that deserve attention
Many serious risks start as ordinary configuration problems. A forgotten remote access service, a weak administrator password or an overly permissive firewall rule can become an entry point. In web environments, poor access controls, injection flaws and session weaknesses may expose accounts or sensitive records.
Network-specific issues often include:
- Unnecessary open ports and services.
- Weak or outdated encryption protocols.
- Poorly configured VPN or remote access controls.
- Flat networks that allow easy lateral movement.
- Default credentials on devices or management interfaces.
- Inadequate logging and alerting.
- Excessive privileges on shared accounts.
The practical implication is simple: remediation should focus on reducing attack paths, not just closing tickets. Fixing one critical exposed service may matter more than addressing several low-impact cosmetic issues. A good report will help teams prioritise by likelihood, impact and effort.
Making penetration testing part of continuous improvement
Penetration testing works best when it feeds a repeatable improvement cycle. Test results should inform patching, configuration standards, secure development practices, monitoring rules and staff awareness. Retesting is important because a fix that looks complete may not fully remove the original risk.
Some organisations are also moving towards more frequent testing models, including Penetration Testing as a Service, where assessments are performed more continuously or around regular changes. This can be useful for fast-moving teams, but the principle remains the same: testing should produce clear insight and measurable remediation, not just activity.
For software teams, penetration testing should complement secure design, code review, dependency management and automated security checks. For infrastructure teams, it should support hardening, segmentation and access control. For leadership, it provides a grounded view of exposure and helps justify investment in the controls that matter most.
Key takeaways
Penetration testing is an authorised security exercise that shows how weaknesses could be exploited in practice. Network penetration testing focuses on infrastructure and attack paths, while website penetration testing and web penetration testing focus on applications, user flows and web-facing logic. External penetration testing shows what an internet-based attacker can see, while internal testing explores what happens after access is gained.
The strongest results come from combining the right scope, skilled testers, appropriate penetration testing tools and a report that leads to action. When treated as part of an ongoing security programme, penetration testing helps organisations reduce risk, strengthen resilience and make better decisions about where to invest next.