ESSENTIAL GUIDANCE · PENETRATION TESTING · 10 min read
Part of Validate insights →Understanding Penetration Hacking Techniques and Tools
Penetration hacking is the controlled practice of thinking and acting like an attacker so an organisation can find weaknesses before a real threat actor does. In a professional setting, it is better known as penetration testing or pen testing, and it combines technical skill, careful planning and clear reporting. This article explains the main techniques, tools, service models and buying considerations so you can approach security testing services with more confidence.
Technical review lead: James Hinton · Offensive security lead
What does penetration hacking actually involve?
Penetration hacking involves authorised attempts to identify, verify and, where appropriate, exploit security weaknesses in systems, networks, applications or physical environments. Unlike a simple vulnerability assessment, which may list potential issues, a well-scoped pentest test examines whether those weaknesses can be used in realistic attack paths and what the business impact could be.
The word “hacking” can sound reckless, but professional pen testing is structured and permission-based. The tester works within an agreed scope, follows rules of engagement and documents findings so the organisation can prioritise remediation. The aim is not to embarrass teams or break systems; it is to provide evidence that helps reduce risk.
A good test usually combines automated checks with manual investigation. Vulnerability management tools can help discover known issues quickly, but experienced testers add context: whether a finding is genuinely exploitable, how it could be chained with other weaknesses, and what fix would make the biggest difference.
Get a free copy of our penetration test scoping workbook
Completing this workbook does not authorise testing. Active testing requires explicit written permission from the relevant system owner.
Need help scoping your penetration test? Contact us for help →
Pen testing follows a clear lifecycle
Although every engagement is different, most pentest services follow a recognisable process. This structure protects the client, guides the tester and ensures the final output is useful rather than just technical noise.
A typical lifecycle includes:
- Scoping and planning – The organisation and tester agree what is in scope, what is out of scope, testing windows, contact points, risk limits and reporting expectations.
- Reconnaissance – The tester gathers information about targets, such as exposed services, application behaviour, domains, technologies and potential entry points.
- Scanning and analysis – Tools are used to map systems and identify likely weaknesses, but results are reviewed carefully to reduce false positives.
- Exploitation – Where authorised, the tester attempts to prove whether a weakness can be used to gain access, escalate privileges or reach sensitive data.
- Post-exploitation assessment – The tester may assess what an attacker could do next, such as moving laterally or maintaining access, within the agreed boundaries.
- Reporting and remediation guidance – Findings are explained by severity, evidence, business risk and practical steps for fixing them.
- Retesting – After remediation, the tester verifies whether key issues have been properly resolved.
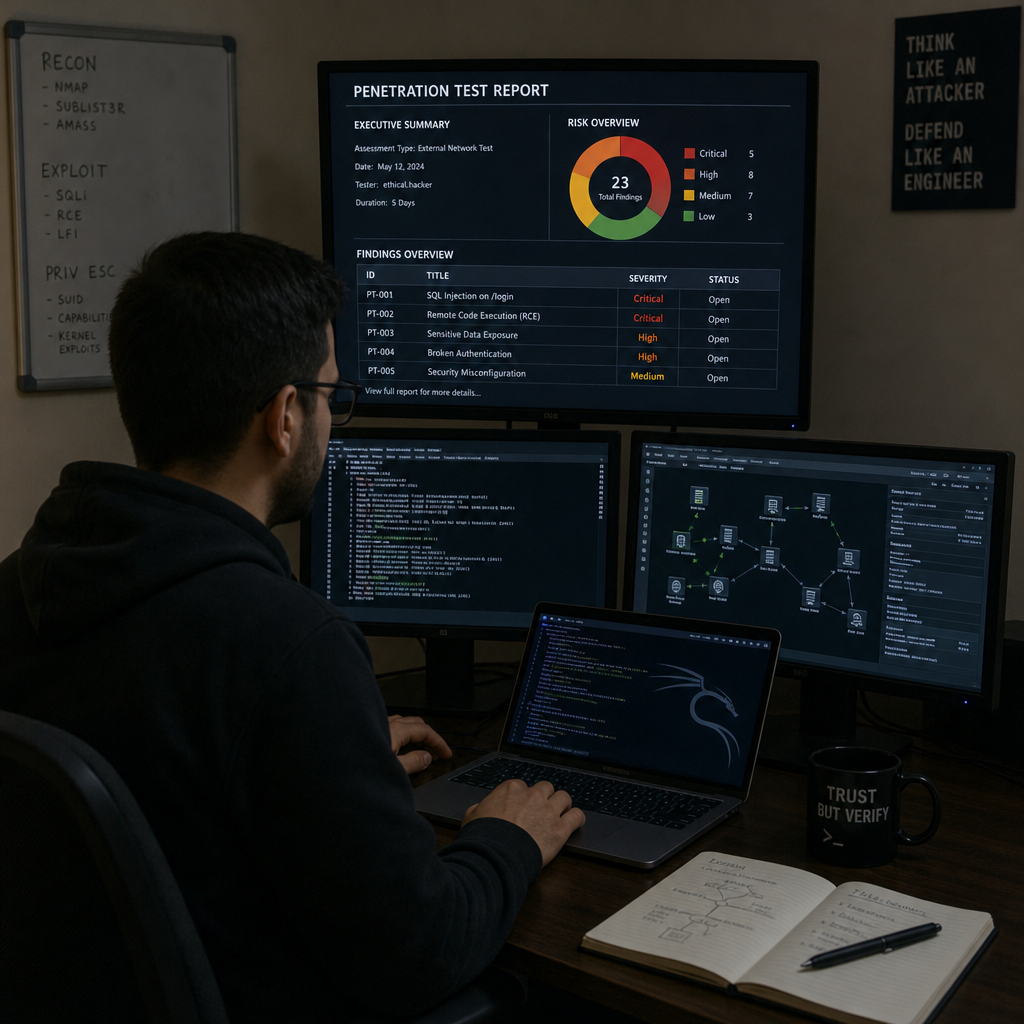
The reporting stage is where the value often becomes visible to non-technical stakeholders. A clear report should help security, IT and leadership teams understand which issues matter most, why they matter and what should happen next.
Main types of penetration testing
Different tests answer different security questions. Choosing the right type matters because a web application test, a wireless test and a social engineering exercise require different skills, tools and safeguards.
Black box, white box and grey box approaches
A black box test gives the tester little or no prior knowledge, simulating an external attacker starting from public information. This can be useful for understanding your exposed attack surface, but it may spend more time on discovery.
A white box test gives the tester detailed information such as architecture diagrams, credentials, source code or configuration details. It is often more efficient for deep technical assurance because the tester can focus on complex weaknesses rather than guessing how the system works.
A grey box test sits between the two. The tester receives partial information, which can reflect a realistic scenario such as a compromised user account, a supplier with limited access or an attacker who has already gathered some intelligence.
Network, application, wireless, social and physical testing
Network penetration testing services focus on infrastructure such as servers, firewalls, cloud networks, VPNs and internal systems. The aim is to discover whether misconfigurations, exposed services or weak access controls could allow unauthorised access or movement through the environment.
Application testing examines websites, APIs and software platforms. A web penetration tester will look for issues such as broken authentication, insecure session handling, access control flaws, injection risks and business logic problems that scanners may miss.
Wireless testing reviews Wi-Fi security, segmentation and access controls. Social engineering tests assess human and process weaknesses, such as phishing resilience or helpdesk procedures. Physical tests, where appropriate, look at whether buildings, devices or restricted areas can be accessed without authorisation.
What tools do penetration testers use?
Penetration testers use a mix of specialist tools, scripts, commercial platforms and manual techniques. Tools do not replace expertise; they accelerate discovery, evidence gathering and analysis.
Common examples include:
- Nmap for network discovery, port scanning and service identification.
- Metasploit for controlled exploitation and validation of known weaknesses.
- Burp Suite and OWASP ZAP for web application testing, proxying traffic and analysing requests.
- Wireshark for inspecting network traffic and investigating protocol behaviour.
- John the Ripper for password auditing in approved test scenarios.
- Vulnerability management tools for tracking weaknesses, assigning ownership and monitoring remediation over time.
The important point is not whether a tester uses a famous tool, but whether they understand its output. Automated results can be incomplete, misleading or too generic. Skilled testers interpret findings in context, safely validate risk and translate technical details into actions the organisation can actually take.
Penetration testing and vulnerability assessment are not the same
A vulnerability assessment identifies and categorises possible weaknesses, while pen testing goes further by testing exploitability and likely impact within an agreed scope. Both are valuable, but they answer different questions.
A vulnerability assessment might tell you that a server is missing a patch, an application header is misconfigured or an old service is still running. Pen testing asks what an attacker could do with those conditions. Could they gain access? Could they escalate privileges? Could they reach customer data or disrupt a business process?
For many organisations, the strongest approach combines both. Routine scanning and vulnerability management provide ongoing visibility, while periodic penetration testing gives deeper assurance and a more realistic view of risk.
| Activity | Best for | Limitation |
|---|---|---|
| Vulnerability assessment | Finding and prioritising known weaknesses at scale | May not prove real-world exploitability |
| Pen testing | Validating attack paths and business impact | Depends on scope, time and tester skill |
| Continuous monitoring | Tracking exposure over time | Still needs expert interpretation and remediation |
| Retesting | Confirming fixes worked | Only covers the remediated items being checked |
Service models: manual, automated, hybrid and continuous
Penetration testing companies may offer different delivery models. Understanding these models helps you choose the right level of assurance for your budget, risk profile and pace of change.
Manual testing is expert-led and best suited to complex environments, business logic, bespoke applications and high-risk systems. It is usually more insightful than purely automated testing because a human tester can adapt, investigate unusual behaviour and chain findings together.
Automated testing is useful for broad coverage, repeatability and speed. It can identify common issues quickly, but it should not be treated as a complete substitute for expert assessment.
Hybrid testing combines automated discovery with manual validation. For many organisations, this is the practical middle ground: efficient enough to cover important assets, but still informed by human judgement.
Continuous or platform-based services are sometimes used by organisations that release software frequently or operate fast-changing cloud environments. These models can help security teams keep pace with change, especially when paired with clear remediation workflows.
Why businesses invest in pen testing
Businesses invest in pen testing because it turns uncertainty into actionable evidence. Instead of relying on assumptions, teams can see where controls work, where gaps remain and which weaknesses could affect operations, data or reputation.
Key motivations include:
- Reducing breach risk by finding exploitable weaknesses before attackers do.
- Protecting sensitive data such as customer records, payment information, employee details or intellectual property.
- Supporting compliance where frameworks, contracts or sector expectations require security assurance.
- Improving incident readiness by testing how teams detect, escalate and respond to suspicious activity.
- Guiding investment so security budgets focus on the most meaningful fixes rather than the longest list of issues.
The business value comes from clarity. A strong report does not simply say “critical vulnerability found”; it explains the route an attacker could take, the potential consequence and the practical steps needed to reduce exposure.
How should you choose penetration testing companies?
Choose penetration testing companies by looking beyond price and asking whether they have the skills, process and communication style to test your environment safely and usefully. For organisations comparing pen testing companies UK-wide, it is sensible to consider relevant certifications, sector experience, reporting quality and how well the provider explains scope.
Useful questions to ask include:
- What testing methodology do you follow, and how is it adapted to our environment?
- Who will perform the work, and what relevant experience or certifications do they hold?
- How do you manage risk during testing to avoid unnecessary disruption?
- Will the report include evidence, severity ratings, business impact and remediation guidance?
- Do you offer a debrief with technical and non-technical stakeholders?
- Is retesting included or available after fixes are applied?
- How do you handle sensitive data discovered during the engagement?
Cost will depend on scope, complexity, access, testing depth and reporting requirements. Rather than seeking the cheapest quote, aim for a provider that can explain exactly what will be tested, what will not be tested and what evidence you will receive at the end.
Turning findings into lasting security improvement
A penetration test is only valuable if the organisation acts on it. The best outcomes happen when findings are assigned to owners, tracked through remediation and verified once fixes are complete.
Start by separating urgent exploitable issues from lower-risk hygiene improvements. Then look for patterns. If several findings relate to weak access control, inconsistent patching or poor configuration management, the root cause may be a process gap rather than an isolated technical mistake.
It is also worth aligning pen testing with broader security work. Development teams can use findings to improve secure coding practices. Infrastructure teams can strengthen hardening standards. Leadership teams can use the results to make better decisions about risk, investment and resilience.
Testing should also happen at sensible intervals. Many organisations test annually, after major system changes, before launching critical applications or when customer, regulatory or contractual expectations require assurance. Higher-risk environments may need more frequent or continuous testing.
Final takeaway
Penetration hacking, when performed ethically and professionally, is one of the most practical ways to understand real security exposure. It goes beyond checklists by showing how weaknesses could be used, what the consequences may be and which fixes deserve priority.
Whether you need network penetration testing services, application-focused pentest services or broader security testing services, the right approach should be scoped, evidence-led and clearly reported. Choose skilled testers, act on the findings and treat pen testing as part of an ongoing security programme rather than a one-off exercise.